On this page
In this article, I am going to explain a security issue that I found on a web site which is famous within the information security researchers. Samy Kamkar is an American privacy and security researcher, computer hacker, entrepreneur and for me a very big influencer. Samy Kamkar is the person who created the first JavaScript-based worm known as Samy Worm which went viral within a few hours ultimately compelling myspace to shut down temporarily.
Viewing the hidden source
I was explaining the work of Samy Kamkar (opens in a new tab) to one of my friends. Samys site has so many easter-egg like challenges. We are not allowed to view the source code using normal methods like ‘right-click’ , ‘Inspect element’ , ‘Ctrl + shift + I’ etc. Then I tried the following snippet.
javascript:https://samy.pl/?%0aalert(document.body.innerText=document.body.innerHTML)I was able to see the source code that was extracted from the DOM for the Samy’s website.
You guys can go to https://samy.pl (opens in a new tab) and try to right-click, view his source code using ctrl + u or even go to another tab and type:
view-source:https://samy.plLastly, try to view the source using inspect element and I think you will be surprised. Do comment if you find any other way to view the source code.
Finding the vulnerable endpoint
Then I started going through everything that was on the website. I saw that he was using JS code to detect proxies like Burp, Charles & Fiddler. I dug deeper to see everything he was using to make the awesome website that he has. Sometime later I found a suspicious “jsonp endpoint” that was used to reflect the public IP address of whoever is requesting his website.
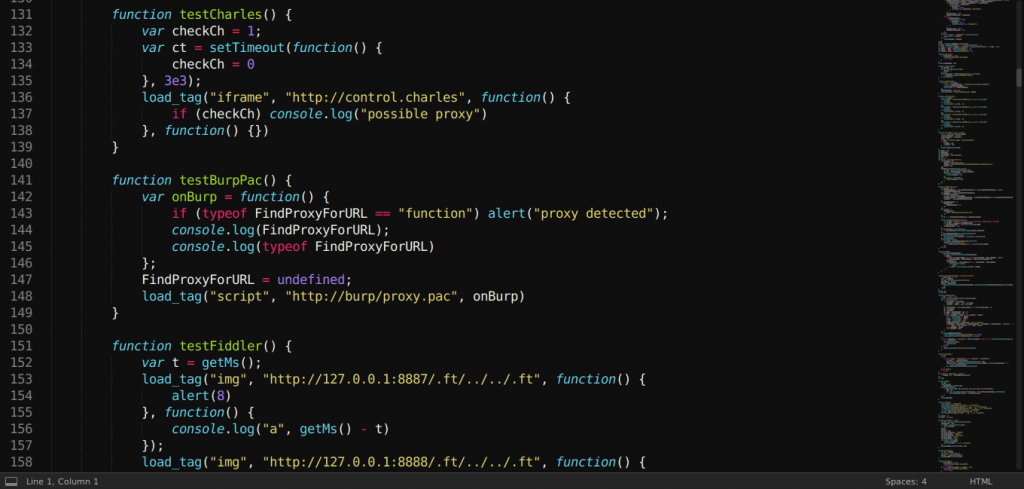
Verifying proxy tools.
This code was verifying if the user was logged in or not.
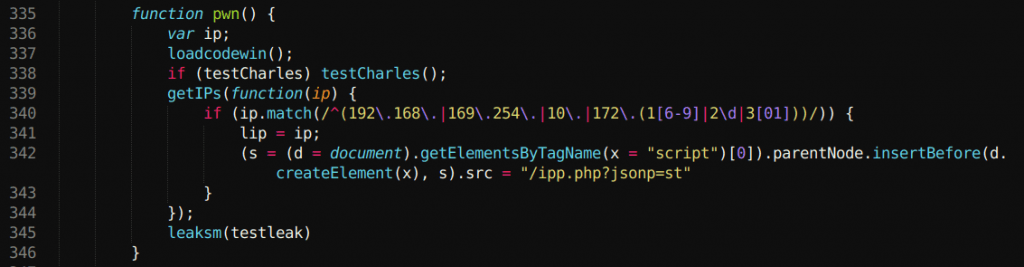
Vulnerable EndPoint
The endpoint was something like https://samy.pl/ipp.php?jsonp=st (opens in a new tab) then it would reflect something like this
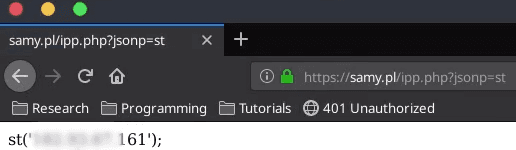
From reflection to XSS
After finding the endpoint I started altering the endpoint. First I removed ‘st’ from the endpoint and I saw that it was also removed on the reflected output.
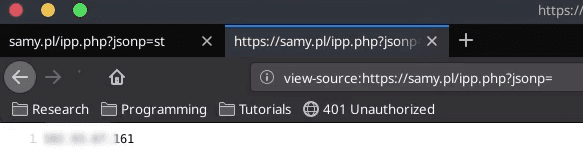
I then altered furthermore by adding ‘<>’ which was successfully reflected on the site.
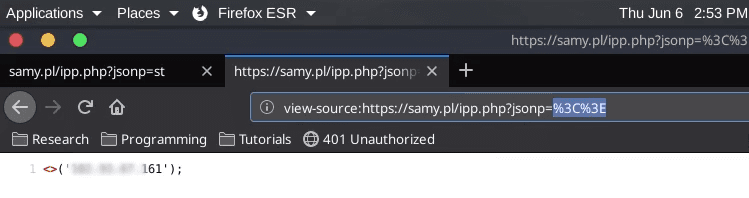
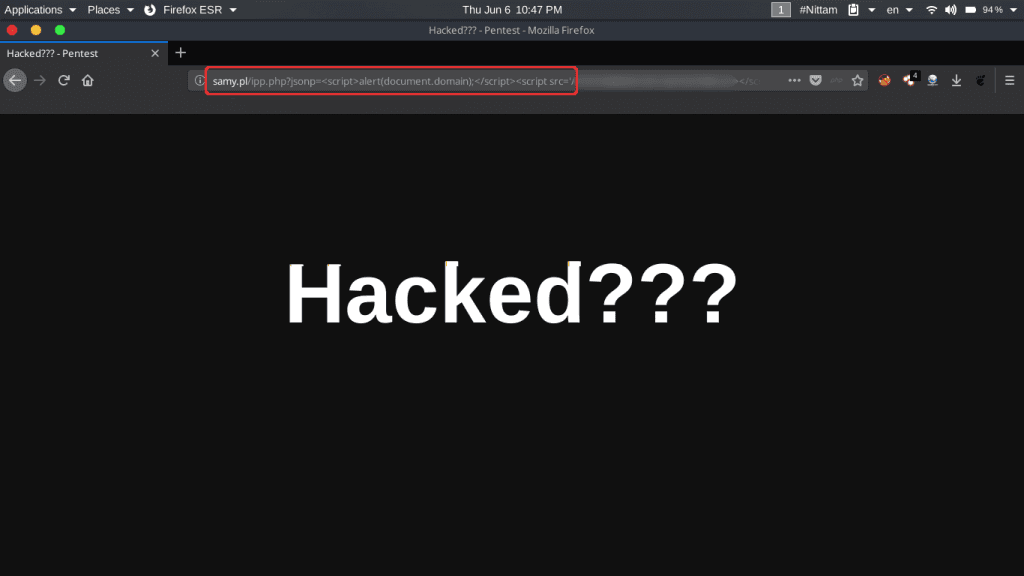
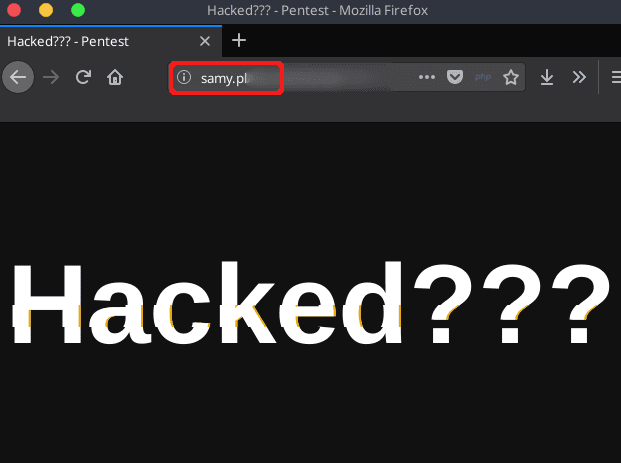
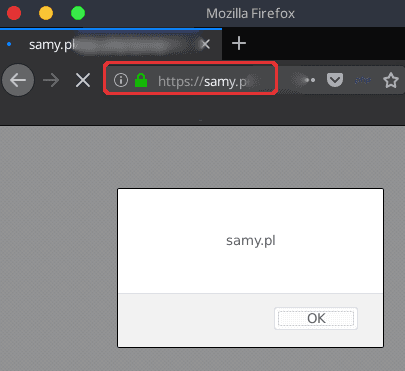
When I saw that the greater than and smaller than symbols were reflected I straight jumped into using my custom script to reflect a cross-site scripting vulnerability that was successfully executed and that was how I was able to perform XSS on Samy.pl.
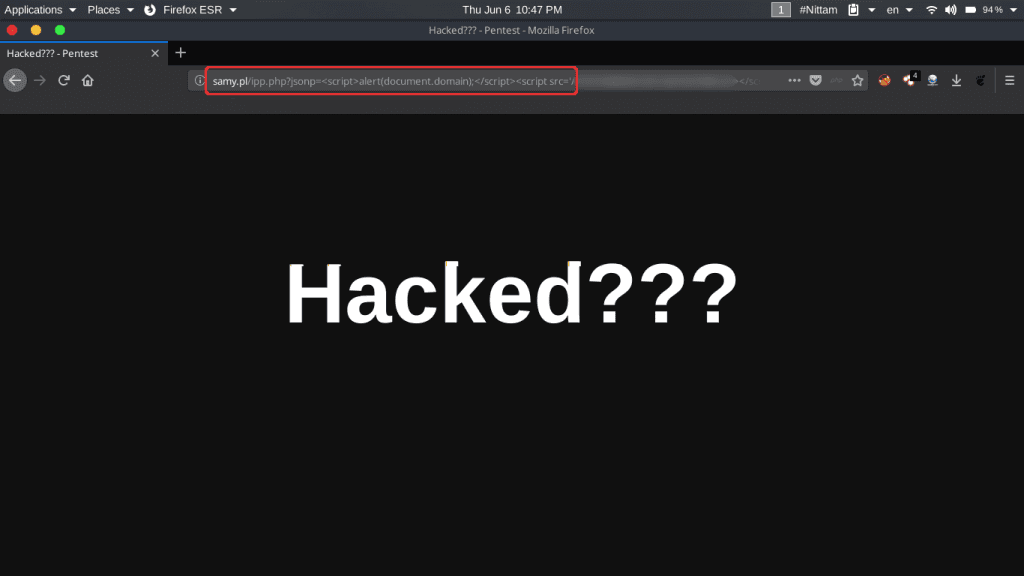
R-XSS DOM Overwrite
Timeline
-
June 6, 2019 — Report Sent
-
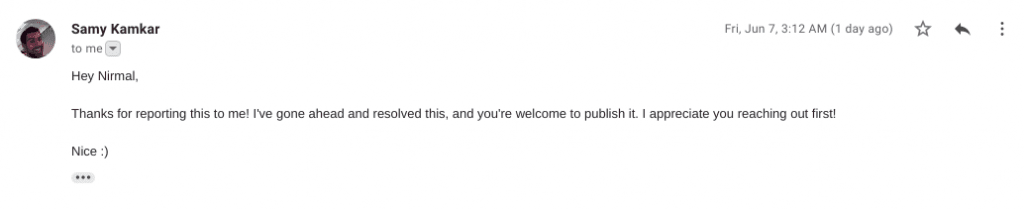
June 7, 2019 — Fixed & allowed to publish by Samy Kamkar
२ शब्द
I have found in my past experience that even some top security researchers from HackerOne have had their site hacked or other security researchers have discovered some type of vulnerability. No matter how much people claim to have their site/system it is 100% secure or no matter how much a person is experienced it is only a matter of time and the amount of knowledge to discover a new or even existing flaw.
Note: I did not think I would find an XSS issue in Samy Kamkar's site. The person who created the first-ever javascript-based worm. I have written this blog with the full permission of Samy Kamkar (opens in a new tab).